
Encountering the message “Compatible TPM cannot be found” inside tpm.msc can disrupt Windows Hello, trigger BitLocker recovery prompts, and block Windows 11 upgrade eligibility. This situation typically indicates that the security processor has been deactivated within the system firmware or that its driver configuration has become corrupted, rather than signifying physical hardware failure.
Trusted Platform Module technology functions as a hardware-based or firmware-based cryptoprocessor that secures cryptographic keys, verifies startup integrity, and supports biometric authentication. Windows 11 strictly mandates version 2.0 to ensure baseline security. Without an active and functional module, security features experience degradation, and upgrade utilities reject the system installation.
Modern architectures integrate this capability directly into the central processing unit. Intel platforms utilize Platform Trust Technology, whereas AMD systems rely on firmware Trusted Platform Module implementations. Motherboard manufacturers occasionally ship systems with these features disabled by default, and routine BIOS updates can unexpectedly revert these configurations back to an off state.
Checking TPM Status
Before modifying any configurations, inspect the current administrative state of the system. Access the management console by pressing the Windows key, typing tpm.msc, and pressing enter. Review the status information displayed in the central portion of the management window.
| tpm.msc message | What it means |
|---|---|
| “The TPM is ready for use” + Version 2.0 | TPM is healthy, skip to the driver or Hello/BitLocker sections if you still have issues |
| “Compatible TPM cannot be found” | TPM is disabled in BIOS or not present, start with Fix #1 |
| “The TPM is ready for use” + Version 1.2 | TPM is on but the wrong version, check BIOS for a version switch |
| TPM console opens but shows errors or warnings | Driver issue, go to Fix #4 |
Understanding Intel PTT and AMD fTPM
Intel Platform Trust Technology operates as a firmware-level security layer integrated into eighth-generation and newer core processors. It fulfills all functional requirements mandated for Microsoft’s operating system without requiring a dedicated hardware module on the motherboard. Users can typically locate this setting within the security, advanced, or platform configuration menus of the system firmware.
AMD firmware security uses a comparable approach across Ryzen processors to satisfy version 2.0 criteria. Certain early implementations of this architecture occasionally generate minor system latency during intensive computational workloads, though this behavior is uncommon. Applying the latest motherboard firmware resolves these rare performance irregularities.
Enabling TPM in BIOS
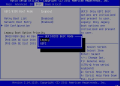
Manufacturer-specific firmware interfaces determine how users access security options. Accessing the configuration interface requires repeatedly pressing the designated manufacturer key during the initial startup sequence. Once inside the utility, navigate to the security or advanced hardware menus to locate and activate the platform trust settings.
After adjusting the configuration parameter, save the modifications and restart the computer normally. Execute the management console command once more to verify that the security processor is recognized and operational.
Reinstalling the TPM Driver
Persistent error messages or yellow warning indicators inside Device Manager point toward a driver communication failure. Expand the Security Devices category within Device Manager to check the operational status of the security processor. If the category itself is missing despite activation in firmware, driver corruption is the primary suspect.
Right-click the device entry and select uninstall device to remove the corrupted driver package. Restart the operating system to force Windows to automatically reinstall the correct device driver upon boot.
Accessing BIOS from Windows 11
Systems that boot too rapidly to register manual keystrokes require an alternative access method. Navigate to the system update and recovery settings within the operating system menu. Selecting advanced startup options forces the machine to restart into the diagnostic environment where firmware access is available.
Restoring Windows Hello
Biometric authentication services store credential data securely within the cryptographic module. Restoring module detection does not automatically re-establish biometric links. Users must manually re-enroll facial recognition or fingerprint credentials through the sign-in options menu.
Resolving BitLocker Encryption Prompts
Drive encryption utilities store recovery keys within the security processor to protect sensitive data. Modifications to the security state caused by firmware toggles or updates will temporarily interrupt this verification process. Entering the designated numerical recovery key restores normal access to the encrypted storage volumes.
Passing the Windows 11 PC Health Check
Upgrade utility blocks regarding security requirements usually trace back to disabled features or outdated version configurations. Verify that both the security processor and Secure Boot remain active within the motherboard firmware interface to satisfy installation prerequisites.
Clearing the TPM
Clearing the security processor resets its operational memory back to a blank factory state. This administrative action resolves persistent initialization faults that survive standard driver reinstallation procedures. Active encrypted drives require a backed-up recovery key before executing this procedure to prevent permanent data lockouts.
Updating System BIOS
Outdated system firmware frequently accounts for undetected security hardware that resists standard troubleshooting steps. Installing the most recent motherboard firmware version from the official manufacturer support portal addresses underlying platform bugs.
Troubleshooting Summary
| Symptom | Likely Cause | Fix to Try |
|---|---|---|
| tpm.msc says “Compatible TPM cannot be found” | TPM disabled in BIOS | Fix #1, #2, or #3 |
| No Security Devices section in Device Manager | TPM disabled in BIOS or driver/OS issue | Fix #1, #2, or #3; then Fix #4 if BIOS shows TPM enabled |
| Yellow warning triangle on TPM in Device Manager | Most often a driver issue; can also be firmware or hardware | Fix #4; if unresolved, check Fix #10 |
| Windows Hello unavailable after BIOS update | TPM reset to off by update | Fix #1 or #2, then Fix #6 |
| BitLocker asks for recovery key on every boot | TPM state changed or cleared | Fix #7 |
| PC Health Check blocks Windows 11 upgrade | TPM off or version 1.2 | Fix #1, #2, or #3 |
| All fixes tried, TPM still not detected | Possible hardware fault | Fix #10 |
Successfully resolving a tpm device not detected error in Windows 11 usually requires nothing more than restoring the active status of the firmware security feature within the system BIOS.